
In this article
- What is Metasploit?
- Core Components of Metasploit
- How Metasploit Works for Ethical Hacking?
- Key Features of the Metasploit Tool
- Benefits of Using Metasploit for Cybersecurity Professionals
- Metasploit Editions: Community, Pro Open-Source
- Real-World Examples of Metasploit in Action
- Conclusion
- Frequently Asked Questions
Do you want to know ‘What is Metasploit?’ and how amazing it can be for penetration testers practicing their skills in the Industry? If yes, then you are at the right place. Several organizations are offering huge working opportunities for pentesting professionals.
In the end, we will introduce you to a reputed training institute offering a dedicated training program related to pentesting skills. What are we waiting for? Let’s get straight to the topic!
What is Metasploit?
Penetration testers utilize Metasploit, an open-source security framework, to find, exploit, and verify vulnerabilities in networks and computer systems. It offers a modular framework that allows ethical hackers to test defenses, automate security assessments, and acquire access by matching different exploits with certain payloads.
Let’s talk in detail about “What is Metasploit?” and explore its benefits!
Core Components of Metasploit
The following are some of the core components of Metasploit:
- Exploits: The "keys" that unlock the door are these. They are made up of code that is intended to exploit a particular weakness in a system, program, or network in order to obtain access.
- Payloads: This is the "package" that the exploit delivers. The payload executes on the target to carry out tasks, like launching a Meterpreter shell or executing custom scripts, after the exploit is successful.
- Auxiliary: These "utility" tools are employed for non-exploitative jobs. Port scanners, service enumerators, password sniffers, and vulnerability testers are a few examples.
- Post-Exploitation (Post): Once a session has been established, these modules are utilized. Deeper operations like obtaining system information, dumping hashes of passwords, and pivoting to additional networked machines are made possible by them.
- Encoders: The purpose of these modules is to "disguise" the payload. To get beyond security measures like antivirus software, they alter the payload's signature.
- NOP Generators: These modules, which stand for "No Operation," fill buffer spaces by generating random padding bytes. For a reliable attack, this guarantees that the exploit code is properly aligned in the system's memory.
How Metasploit Works for Ethical Hacking?
|
S.No. |
Steps |
How? |
|
1. |
Reconnaissance & Scanning |
Testers scan target systems for open ports, active services, and known vulnerabilities using "Auxiliary" modules (sometimes incorporating results from tools like Nmap). |
|
2. |
Vulnerability Analysis |
To find possible "Exploits" that fit the target's vulnerabilities, the collected data is cross-referenced with Metasploit's extensive database. |
|
3. |
Exploitation |
The tester pairs a Payload (the action code) with a particular Exploit (the entrance method). The framework tries to compromise the target by executing the exploit command. |
|
4. |
Establishing a Session |
If the payload is successful, it establishes a connection, typically a Meterpreter shell, that allows the hacker to access the victim's computer remotely. |
|
5. |
Post-Exploitation |
"Post" modules are then used by ethical hackers to obtain additional proof, test privilege escalation (obtaining admin rights), or show how an attacker could penetrate farther into the network ("pivoting"). |
|
6. |
Cleanup & Reporting |
Lastly, the tester eliminates any temporary files or backdoors and uses the results to create a report that aids the company in fixing any vulnerabilities found. |
Key Features of the Metasploit Tool
The following are the key features of the Metasploit tool:
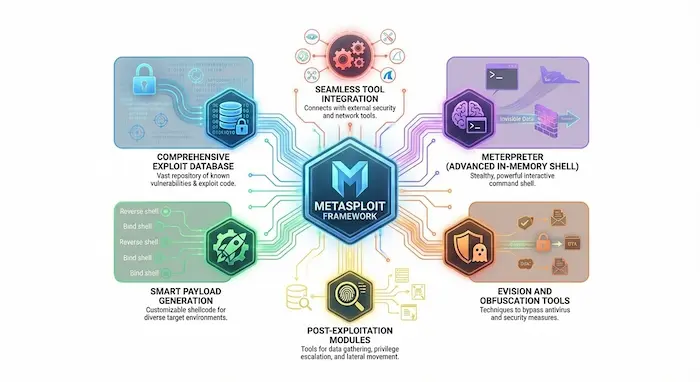
● Comprehensive Exploit Database: Contains thousands of tested, pre-configured modules that target known vulnerabilities on a variety of platforms, including Windows, Linux, and Android.
● Smart Payload Generation: Automatically generates unique malicious code (payloads) to carry out tasks on a target, like launching automated scripts or opening remote shells.
● Meterpreter (Advanced In-Memory Shell): A sophisticated, interactive payload that offers deep control without leaving forensic evidence on the hard disk by completely residing in the target system's memory.
● Evasion and Obfuscation Tools: Include NOP generators and encoders that change the exploit code signature to get beyond network security filters and antivirus software.
● Seamless Tool Integration: Creates a unified testing workflow by seamlessly integrating with various cybersecurity tools, such as Nessus for vulnerability identification and Nmap for scanning.
● Post-Exploitation Modules: Offers specific modules that allow users to "pivot" over the network after gaining initial access, dump password hashes, and elevate user rights.
Benefits of Using Metasploit for Cybersecurity Professionals
|
S.No. |
Benefits |
How? |
|
1. |
Efficiency & Automation |
By automating routine operations like host finding, port scanning, and vulnerability testing, it replaces laborious human procedures. |
|
2. |
Standardization of Exploits |
It guarantees that testers utilize "safe" code that won't unintentionally damage a client's production system by offering a dependable, tested repository of more than 2,000 exploits. |
|
3. |
Hands-on Skill Development |
It is an effective training tool for understanding how actual attackers navigate a network, escalate access, and steal data. |
|
4. |
Stealth Testing |
Professionals can verify the effectiveness of an organization's security team and detection tools (such as IDS/IPS) with its integrated encoders and evasion modules. |
|
5. |
Customizability |
Because it is open-source, experts can create their own Ruby scripts or alter pre-existing modules to fix special, proprietary vulnerabilities discovered during an engagement. |
|
6. |
Detailed Reporting Evidence |
The approach facilitates the documentation of the complete "kill chain" from initial entry to lateral migration, giving stakeholders tangible evidence of danger. |
|
7. |
Collaboration |
Multiple pentesters can work on the same target network at once because of its integration with team-based tools like Armitage and Metasploit Pro. |
Metasploit Editions: Community, Pro & Open-Source
The following are the Metasploit editions:
a) Community: A free web-based graphical user interface (GUI) intended to make vulnerability verification and network discovery easier for novice users. (Note: In 2019, Rapid7 stopped issuing new licenses for the Community version, encouraging customers to switch to the open-source Framework).
b) Pro: Web application scanning, automated processes, and sophisticated reporting for enterprise security teams are all included in the flagship commercial edition. It has specific "MetaModules" for things like VPN pivoting to test hidden network portions, automated brute-forcing, and phishing simulations.
c) Open-Source (Metasploit Framework): The project's central command-line tool, which offers complete access to thousands of exploit modules and the source code. For security researchers who need fine-grained control and the ability to manually alter payloads and exploit modules, it is the recommended tool.
Real-World Examples of Metasploit in Action
|
S.No. |
Examples |
What? |
|
1. |
Verifying Critical Legacy Flaws (EternalBlue) |
Global ransomware like WannaCry was driven by the "EternalBlue" exploit, which was leaked in 2017. Security experts now employ Metasploit's ms17_010_eternalblue module to demonstrate to stakeholders that unpatched legacy Windows systems are still susceptible to immediate, remote administrative takeover. |
|
2. |
Demonstrating Web Application Breaches (Struts/ Tomcat) |
Pentesters attack out-of-date web server software (such as Apache Struts) using Metasploit modules. The tester can use a Meterpreter payload to demonstrate how an attacker could enter the company's private internal database via a publicly accessible website by taking advantage of an unpatched remote code execution vulnerability. |
|
3. |
Internal Network Pivoting during Audits |
A simple phishing payload created by msfvenom could allow a tester to access a low-security workstation during a multi-stage audit. They then turn the workstation into a gateway using Metasploit's "pivoting" capability, which enables them to attack higher-value targets (such as domain controllers) that are normally protected by internal firewalls. |
Conclusion
Now that we have talked about “What is Metasploit?”, you might want to learn how to use it professionally. For that, you can get in contact with Craw Security, offering the Advanced Penetration Testing Course Training with AI in Delhi to IT Aspirants.
During the training sessions, students will be able to try their skills while using Metasploit under the supervision of penetration testing professionals. Moreover, online sessions will facilitate students in remote learning.
After the completion of the Penetration Testing Course Training with AI in Delhi offered by Craw Security, students will receive a certificate validating their honed knowledge & skills during the sessions. What are you waiting for? Contact, Now!
Frequently Asked Questions
About What is Metasploit?
- What is the Metasploit tool?
Penetration testers utilize Metasploit, a modular open-source security framework, to find, exploit, and validate vulnerabilities in networks and computer systems.
- What is the primary purpose of the Metasploit Framework?
The Metasploit Framework's main goal is to give security experts a complete, modular platform to find, exploit, and validate vulnerabilities in computer systems and networks.
- Is Metasploit legal to use for ethical hacking?
Metasploit can only be used lawfully if you have the system owner's express written consent to conduct testing within a narrowly specified scope.
- How does Metasploit work during penetration testing?
In the following ways, Metasploit works during penetration testing:
a) Information Gathering,
b) Exploitation,
c) Post-Exploitation, and
d) Reporting.
- What are the main features of the Metasploit tool?
The following are the main features of the Metasploit tool:
a) Vast Exploit Database,
b) The Meterpreter Payload,
c) Flexible Payload Generation,
d) Evasion & Anti-Virus Bypass, and
e) Post-Exploitation Capability.
- What types of attacks can Metasploit simulate?
Metasploit can simulate the following types of attacks:
a) Remote Code Execution (RCE),
b) Web Application Exploitation,
c) Social Engineering & Phishing,
d) Client-Side Exploits, and
e) Post-Exploitation & Pivoting.
- What operating systems support Metasploit?
A cross-platform program, the Metasploit Framework is compatible with Windows, Linux (including Kali, Ubuntu, and Red Hat), and macOS.
- What is the difference between Metasploit Community and Metasploit Pro?
The primary distinction is that Metasploit Pro is a commercial enterprise edition with extensive automation, social engineering toolkits, and compliance-ready reporting, whereas Metasploit Community provides a free, basic web-based interface for vulnerability verification and discovery.
- Why do cybersecurity professionals use Metasploit?
Metasploit simulates real-world cyberattacks in a controlled and permitted environment, allowing cybersecurity experts to proactively find, test, and validate vulnerabilities in systems.
- Can beginners learn Metasploit easily?
By beginning with basic scanning modules and using vulnerable lab settings like Metasploitable to safely practice the command-line interface, beginners can easily learn Metasploit.
- Does Metasploit come with pre-built exploits and payloads?
Yes, the Metasploit Framework has an extensive collection of approximately 600 payloads and over 2,100 pre-built exploits that may be used against a variety of operating systems and services.
- How often is Metasploit updated with new modules?
Through its open-source repository on GitHub, the Metasploit Framework is updated nearly every day. Rapid7 provides weekly wrap-ups and bigger formal stable releases.
Want to build a career in cyber security?
Talk to our counsellors about courses, batches and fees. Free demo class available.


